A complete AI policy
18 sections, from the governance committee and risk tiers to data rules and incident response. Sent to you as an editable template after the session.
FREE LIVE WEBINAR · THURSDAY, OCTOBER 22 · 1:00 PM ET · 90 MINUTES
Your staff are already using AI. Learn how to govern it with the compliance program you already run, without building a new framework, and watch the Microsoft tools that enforce it, live.
Free. Can't make it live? Register anyway and we'll send you the recording and the policy template.
18 sections, from the governance committee and risk tiers to data rules and incident response. Sent to you as an editable template after the session.
Green for low-risk uses, approved in days. Yellow for tools that touch patient data, approved with conditions. Red for anything that affects care, coverage or claims, reviewed by your committee.
See how Microsoft Purview and Defender find the AI in use and stop patient data from leaving, often on licenses you already pay for.
The fines don't come from "using AI." They come from the HIPAA failures regulators already penalize, and AI makes them easy to repeat: patient data sent to a vendor with no BAA, tools missing from the risk analysis, and nobody reviewing activity.
Penalties from HHS Office for Civil Rights resolution agreements and civil money penalties.
After an incident, the first question will be "show me your controls."
Before the session, we asked the healthcare compliance and operations leaders who registered where their AI governance stands today.
83%
don't have AI governance in place yet
"Time."
"Getting senior leaders on board."
"I'm concerned about data privacy overlap between AI used for personal use and business use."
"There is no unified AI regulatory framework in healthcare."
This session is built around those answers: a framework you already know, a policy you don't have to write from scratch, and a way to see and stop shadow AI.
Survey results and the real HIPAA enforcement cases behind the risk
AI governance mapped onto the OIG's seven elements of an effective compliance program, the standard your program is already measured against
All 18 sections of a complete AI policy: committee, risk tiers, vendors and BAAs, data rules, human oversight, patient consent, monitoring and incidents
Find the AI in use across your organization, turn it into an inventory, and block patient data from reaching consumer AI tools
A self-check: how many of the 18 sections could you show an auditor today? And how we help teams close the gaps
Your questions, answered live
A policy in a PDF doesn't stop a paste at 9 p.m. In the demo, Ivan plays a nurse at the end of a shift who pastes a fictional patient note into an AI tool to draft a discharge summary.
Every AI app your managed devices talk to, with users, traffic and a risk score. Shadow AI, made visible.
The paste containing a Social Security number, diagnosis codes and a medical record number is stopped. The same note, de-identified, goes through. The rule stops patient data, not AI.
What compliance sees afterwards: who, when, which site, which rule. Your activity review and your audit evidence.
Shown on Microsoft 365. Some features need specific licenses or add-ons, and we'll tell you which. Not on Microsoft? The policy works on any platform.
Built on the OIG's seven elements of an effective compliance program, the Joint Commission and CHAI responsible-AI guidance, and the healthcare usage rules of Microsoft, Google, OpenAI and Anthropic. Written for any healthcare organization, with clinical-only parts clearly marked.
A starting point for your organization, not legal advice. Have your counsel review it before adoption.
WHEN YOU WANT HELP PUTTING IT IN PLACE
The template saves you the writing. The real work is adapting it to your organization, finding out what AI is actually in use, and setting up the controls that enforce it. Demigos does that with your team, in two steps.
3 weeks · a clear picture of where you stand
We review your policies, interview your compliance, IT, privacy and operations leads, and look at your Microsoft environment read-only to see which AI tools are really in use. Then we tell you where you stand and what to fix first.
We build it with you
We adapt the policy and committee charter to your organization, set up the approval path and inventory, configure Microsoft Purview and Defender to find shadow AI and block patient data from leaving, and train your staff.
No access to patient records. Microsoft discovery is read-only. This is a governance assessment, not legal advice or a certification.
Webinar attendees can book a free 30-minute call to talk through where they stand and whether an assessment makes sense.
Not a hospital? No board? The policy says "patients or members" and "board or owners", and marks the clinical-only parts, so it fits any healthcare organization.
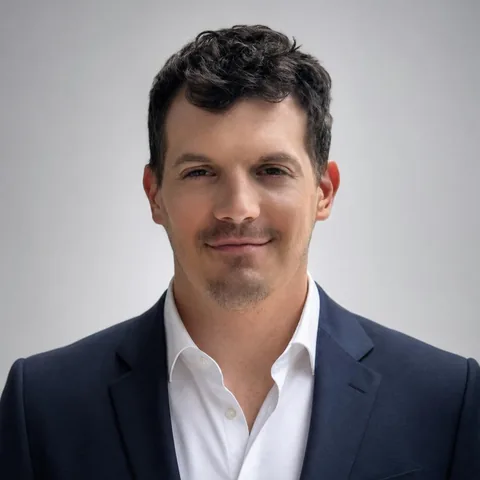
Founder & CEO, Demigos
LinkedInIvan has spent 14+ years building software and 6+ years building AI for healthcare: clinical documentation, prior authorization, care gap detection and revenue cycle. His team has delivered 60+ implementations across health systems, revenue cycle organizations and healthtech companies. He has seen AI adopted with governance and without it, and this session is what he wishes every healthcare leader had before the first tool went live.
Ivan leads the AI in Practice program for healthcare executives. The policy structure was reviewed with a US healthcare attorney.
 Play video: Revenue cycle company
Revenue cycle company
The CRO built AI agents that save his team 10–15 hours a week, then rolled out a compliance agent to his compliance team.
 Play video: Rural hospital
Rural hospital
The CEO set up an AI governance committee and an AI strategy.
Yes. Attending is free, and so is the 18-section policy template.
Yes. Everyone who registers gets the recording and the template, whether or not they attend live.
The first hour is the substance: the framework and all 18 policy sections. Then the live demo, a short look at how to close your gaps, and open Q&A. Stay for as much as you need.
Yes. Near the end, Ivan explains how Demigos runs a 3-week AI Governance Gap Assessment and then helps set up the policy and the Microsoft guardrails. Attendees can book a free 30-minute call to see if it fits. The template and everything shown in the session are yours either way.
Yes. Registrants include revenue cycle and risk adjustment firms, a management services organization, a medical supplier, a pharmaceutical company and consultants. If you handle patient data or touch claims, you have the same exposure. Clinical-only parts are marked.
The policy and the approval path work on any platform. The demo uses Microsoft 365 because many US healthcare organizations run on it, and Ivan will point to alternatives for other environments.
Not for everything. Some controls need E5 or paid add-ons. The session is clear about which features need which license, so you know what you already own.
No. Ivan is a practitioner who builds AI systems for healthcare. The policy structure was reviewed with a US healthcare attorney, but your counsel should confirm how it applies to your organization.
Yes, please do. AI governance needs compliance, IT and operations working together. Share this page or forward your confirmation email.
Online, on TODO: [platform]. Your joining link arrives by email after you register, with a reminder before the session.
Thursday, October 22, 2026 · 1:00 PM ET (10:00 AM PT) · 90 minutes · Free · Online
Register once and you'll get the joining link, a reminder, the recording and the 18-section policy template.